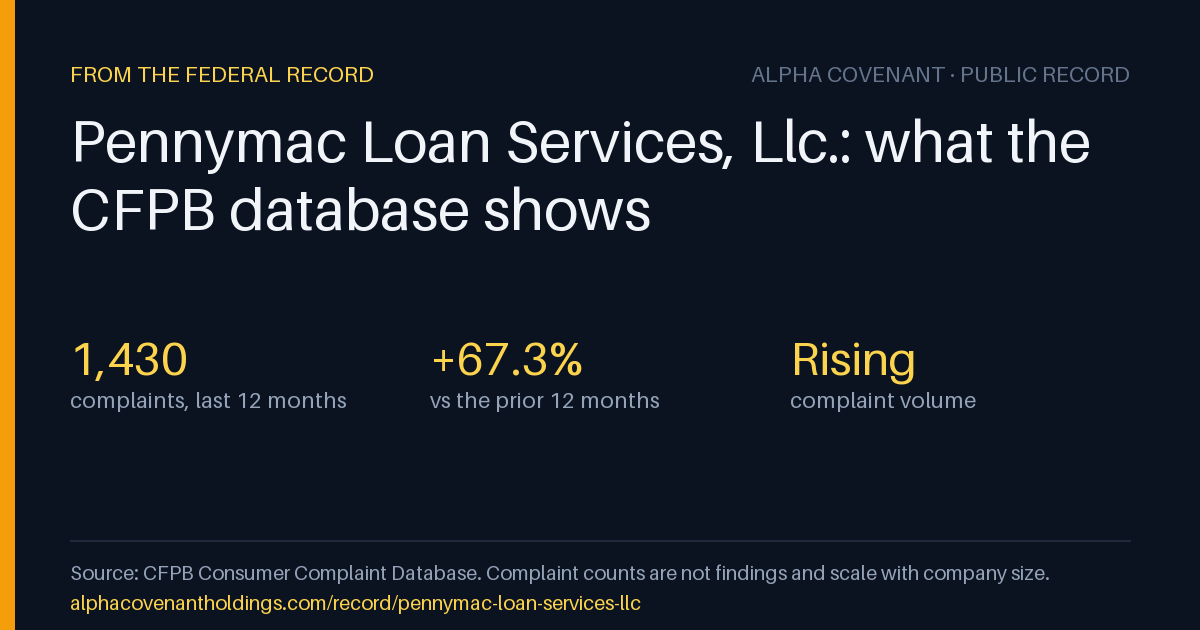
PENNYMAC LOAN SERVICES, LLC.
HHS-OIG exclusion list (LEIE)
No entry under this exact name in the OIG file fetched 2026-11-01.
An entry means OIG excluded this business name from participation in federal health care programs under the cited authority; a reinstatement date means the exclusion ended. No entry under a name means only that this exact name is not in the file — it says nothing about other names, owners or affiliates, and is not a statement of compliance.
Matched on: exact business name as printed in the OIG file (case-insensitive). Source: HHS Office of Inspector General — LEIE (monthly downloadable file) · file fetched 2026-11-01 · recheck at OIG ↗ · what the authority codes mean ↗
Federal contracts and recipient identity (USAspending.gov)
Exploited vulnerabilities in this vendor's products — CISA KEV
No KEV entry names “PENNYMAC LOAN SERVICES, LLC.” as vendor (exact name). Search the catalog for brands or subsidiaries.
Health-record breach reports filed by this entity — HHS OCR
No report under OCR review lists “PENNYMAC LOAN SERVICES, LLC.” as the covered entity (exact name; reports submitted in the last 24 months).
cyber-2026-06: a breach report is attributed only where the covered entity name filed with OCR equals the entity's name after removing corporate suffixes. A breach report is the entity's own notification to HHS under the Breach Notification Rule, listed while OCR reviews it. It is not a finding of fault. Only breaches affecting 500 or more people appear; resolved cases move to OCR's archive, which is not included here.
Source: HHS Office for Civil Rights — Breach Portal (cases currently under investigation)
Single-audit filings (Federal Audit Clearinghouse)
No single-audit filing is on file for this exact name. Entities below the federal-spending threshold do not file; this is not a finding.
A single audit is the auditee's own annual filing, prepared by its independent auditor, required when it spends $750,000 or more in federal awards in a year ($1,000,000 from FY2025). A finding, material weakness or going-concern note is what the auditor reported; it is not a finding of mismanagement by Alpha Covenant, and the filing does not say whether the issue was later resolved.
Source: Federal Audit Clearinghouse (GSA) — single audit filings under 2 CFR 200 Subpart F · pulled 2026-11-03 17:40 UTC
Report a wrong figure — free, logged publicly
Every figure above is an official public record with its source named. Records are records: complaints are not findings, payments are disclosed and legal, adverse-event reports are unverified. Not medical, legal, or financial advice. Nothing here can be changed by payment. How we source this →
Share or embed this Record
Free to reuse with the link intact. The badge and card show the official record and update daily. Payment cannot change them.